The Multi-Trillion Dollar Arms Race Nobody Wins
Global IT spending just smashed through the $5.1 trillion mark. A massive chunk of that capital is currently being desperately shovelled into cybersecurity budgets by terrified chief executives. Let’s be real—the traditional firewall died years ago. The concept of a secure network perimeter completely evaporated the exact moment generative AI and fifty billion connected IoT devices became standard operational infrastructure. Today’s threat actors rarely bother trying to brute-force a network. The reality is that cartels simply log in using stolen credentials or deploy autonomous bots. Chief executives are finally waking up to a harsh operational truth. We are witnessing a fundamental, irreversible pivot away from static prevention mandates toward active, heavily regulated cyber resilience.
Corporate boards now recognize that digital security is not just an IT problem. The infrastructure serves as the absolute bedrock of consumer finance, critical infrastructure, and brand survival. The World Economic Forum’s latest outlook highlights this boardroom panic beautifully. A staggering 87% of organizations are currently flagging AI-related vulnerabilities as their fastest-growing threat. Advanced syndicates routinely bypass legacy defenses by exploiting human identity and manipulating the very automated systems designed to protect us.
Agentic AI and the Death of “Time to Detect”
Artificial intelligence essentially democratized cyber warfare overnight. The defining headache for defenders in 2026 is the rapid deployment of autonomous “agentic” AI within attack ecosystems. Malicious bots tirelessly probe API endpoints while human security teams sleep. These autonomous scripts sniff out complex logical weaknesses that legacy vulnerability scanners routinely miss. Frankly, static scanning is a relic of a bygone era.
Modern Security Operations Centers have completely abandoned periodic checks in favor of Continuous Threat Exposure Management (CTEM). The only operational metric that actually matters anymore is your “time to remediate.” Look closer and you will notice a much darker, structural trend emerging in the form of data poisoning. Sophisticated attackers no longer just exfiltrate sensitive databases. Hackers intentionally corrupt the training datasets of machine learning models. Syndicates embed dormant backdoors directly into the unstructured text and video used for large language model training. A paranoid layer of governance is now required to constantly validate generative models against tampering.
Post-Quantum Cryptography: The Ticking Encryption Bomb
While AI is causing immediate chaos, the impending reality of quantum computing casts a massive, existential shadow over the global financial system. Quantum processors possess the theoretical capacity to instantly shatter the RSA and Elliptic Curve encryption algorithms currently protecting global internet traffic. This is no longer a fun debate for academic cryptographers. Highly organized state-sponsored syndicates are currently executing “harvest now, decrypt later” campaigns at an industrial scale.
Malicious actors actively siphon petabytes of encrypted consumer data and toss it into massive storage lakes. Cartels know perfectly well that mature quantum computers will crack those files within the decade. Enterprise risk managers are consequently scrambling to migrate their architecture to post-quantum cryptographic algorithms recently approved by NIST. The logistical nightmare of migrating an entire Fortune 500 company to Machine Learning-driven Digital Signature Algorithms (ML-DSA) is staggering. The financial realities are brutal. Hardware replacement and cryptographic key overhauls cost major global banks upwards of $100 million per transition cycle. The alternative, however, is a catastrophic loss of institutional trust.
The Password Graveyard and the FIDO2 Rescue Mission
All the advanced encryption in the world means nothing if your front door is wide open. The human element remains our most glaring architectural vulnerability. SecurityWeek data confirms that 75% of all corporate breaches currently stem from compromised identities utilizing perfectly valid credentials. Last year alone, dark web marketplaces traded over six billion passwords stolen specifically by “fraud-as-a-service” infostealer malware.
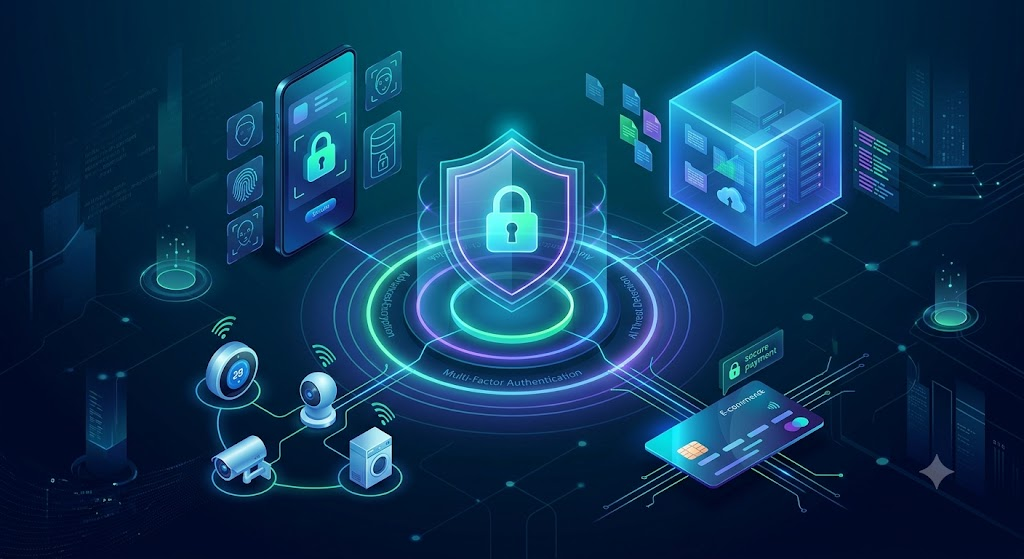
Basic SMS two-factor authentication has been rendered largely useless by adversary-in-the-middle phishing kits. The tech industry’s coordinated response is an aggressive, merciless rollout of FIDO2-certified passkeys. A cryptographic private key is now locked securely inside your smartphone’s physical hardware. You unlock it locally via a biometric fingerprint or facial scan. This shift eliminates the centralized password database entirely. There is simply nothing left on the server for a hacker to steal. Over five billion passkeys are currently active globally. This massive migration drags user authentication out of the dark ages while dropping enterprise help-desk ticket costs by forty percent in the process.
Synthetic Humans and the Biometric Bypass
The inevitable result of locking the front door is that attackers move upstream. Fraud syndicates now weaponize deepfakes to aggressively bypass Know Your Customer (KYC) onboarding protocols. Malicious actors splice legitimate, unmonitored Social Security fragments with fabricated AI faces to birth completely fictitious synthetic identities. Financial losses tied directly to synthetic fraud jumped 50% recently, draining over $3 billion from unsecured credit markets in just twenty-four months. Fraudsters patiently cultivate these phantom personas for years, artificially inflating their credit scores before executing massive, coordinated bust-out schemes.
The catch? These syndicates are not just holding a printed photo up to a webcam to fool an ID check. Attackers deploy deepfake injection malware to intercept a device’s data feed at the operating system level. Synthetic video streams are fed directly into a platform’s camera API to bypass basic verification. To survive this existential threat to digital trust, high-stakes platforms have integrated ISO-certified Level 2 liveness detection. These AI biometric engines evaluate micro-expressions, skin texture, and real-time corneal light reflection. The algorithm mathematically proves a living human is physically present in three-dimensional space.
Zero Trust and the iGaming Compliance Blueprint
“Never trust, always verify” has officially transitioned from a vendor marketing slogan into a binding legal mandate. Zero Trust Architecture (ZTA) operates on the depressing but accurate assumption that a network breach is inevitable. Every single access request is dynamically scrutinized against real-time adaptive risk signals. Your IP geolocation, device health, and even your typing cadence are evaluated instantly. If your behavior deviates slightly from historical norms, the system throws you into a sandboxed environment.
If you want to see this implemented flawlessly under immense pressure, look at the sports betting and iGaming sector. In the first half of 2025 alone, global casino operators bled roughly $160 million in regulatory penalties for failing strict KYC audits. These operators process massive financial volumes under the most fragmented, localized regulatory microscope on the planet. Jurisdictional boundaries force platforms to deploy aggressive geolocation engines that utilize Wi-Fi triangulation and hardware fingerprinting to actively block advanced VPNs. A heavily regulated platform like DraftKings Casino handles this friction natively. The infrastructure utilizes deep TLS encryption, tokenized payment gateways that align with PCI DSS v4 standards, and real-time behavioral telemetry without suffocating the end user. It takes serious engineering capital to build a compliant digital fortress that still feels like a seamless mobile entertainment app.
The Invisible Fortress Mandate
The era of treating cybersecurity as an annoying IT overhead expense is permanently closed. Regulatory bodies across the globe are no longer accepting passive compliance checklists or generic security audits. Governments demand continuous, immutable proof of active data governance. Whether an enterprise is dodging localized state laws in the US or navigating India’s aggressive DPDP framework, the financial cost of a single infrastructure misconfiguration is now measured in nine-figure fines.
Survival over the next three years requires a brutal reimagining of the user lifecycle. The platforms that dominate the market will not just be those holding the heaviest post-quantum encryption keys. Market leadership inherently belongs to the organizations that can successfully camouflage military-grade, zero-trust data defense behind a completely invisible, frictionless consumer interface.